Information Security Policy
Description
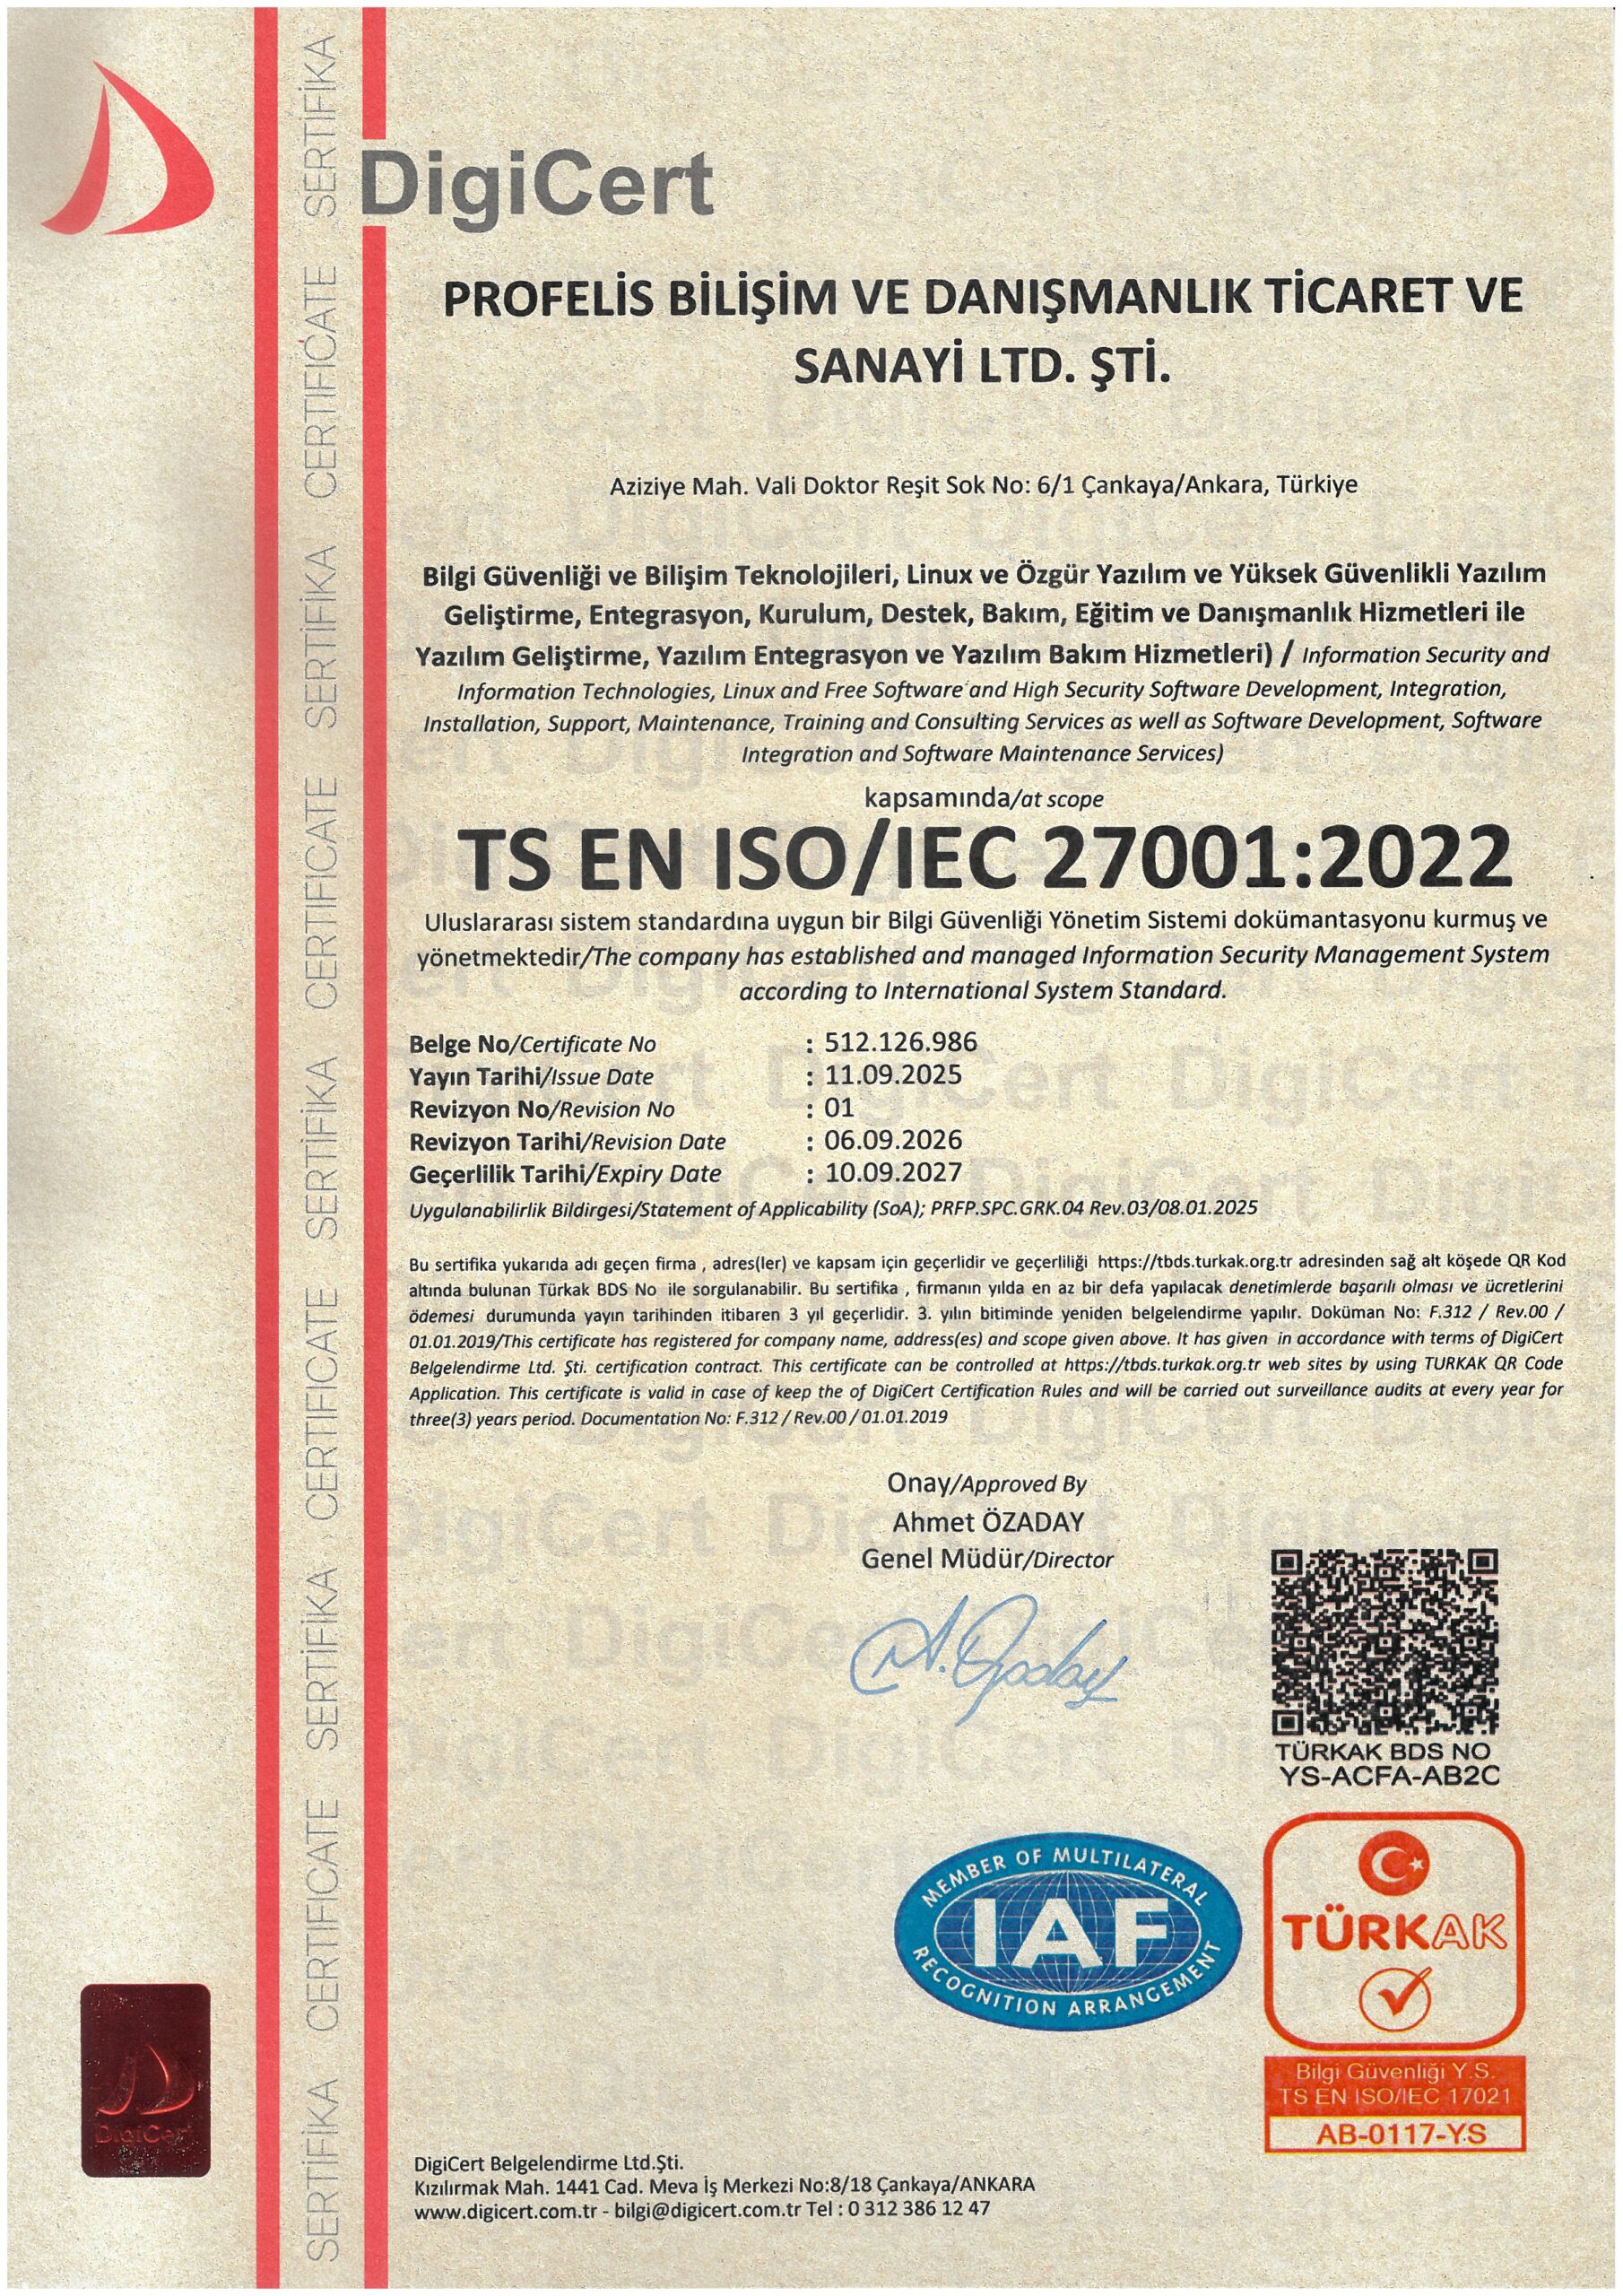
Profelis has been audited by a TURKAK-accredited organization and certified as compliant with the ISO 27001:2022 Information Security Management System standard.
Our Information Security Policy
Our primary objective is to maintain the trust of the institutions and organizations we serve and to ensure a high level of security for the information assets we use in delivering our services.
In this context, our relationships with the customers, institutions, business partners, and companies whose products we distribute are highly valuable to us.
The continuity of the services we provide, the confidentiality of the information we hold, and the integrity of the information assets belonging to both our customers and our company are of great importance.
In this context;
- We are committed to providing services in compliance with applicable laws and regulations, continually enhancing our practices in line with the ISO 27001:2022 standard, and continuously improving the effectiveness of the system.
- We continuously review risks and implement appropriate controls for risks that exceed acceptable levels.
- We maintain a high level of information security awareness among our employees.
- We review our Information Security Management System and Information Security Policy annually to ensure that they remain up to date.
About the Document
With its ISO 27001:2022 certification, Profelis has confirmed the quality of its work in the fields of INFORMATION SECURITY AND INFORMATION TECHNOLOGIES, LINUX, OPEN SOURCE SOFTWARE AND HIGH-SECURITY SOFTWARE DEVELOPMENT, INTEGRATION, INSTALLATION, SUPPORT, MAINTENANCE, TRAINING AND CONSULTANCY SERVICES, as well as SOFTWARE DEVELOPMENT, SOFTWARE INTEGRATION AND SOFTWARE MAINTENANCE SERVICES.
